ISO 27001 Certification in Australia: Strengthening Information Security and Data Protection
In today’s digital world, protecting sensitive business information has become a major priority for organisations across Australia. With increasing cyber threats, data breaches, and growing concerns about information security, businesses need a reliable framework to safeguard their valuable information assets. ISO 27001 Certification Australia helps organisations establish, implement, maintain, and continually improve an effective Information Security Management System (ISMS).
ISO 27001 is an internationally recognised standard that provides guidelines for managing information security risks. It helps businesses identify potential threats, protect confidential information, and maintain the confidentiality, integrity, and availability of data. Organisations across various industries, including IT, healthcare, finance, education, manufacturing, and professional services, can benefit from implementing this standard.
Importance of ISO 27001 Certification in Australia
Australian businesses handle large volumes of confidential information, including customer records, financial details, employee information, and business data. Without proper security controls, organisations may face cyberattacks, unauthorised access, financial losses, and reputational damage.
Achieving ISO 27001 Certification Australia demonstrates an organisation’s commitment to protecting sensitive information through a structured security management framework. It also helps businesses strengthen customer confidence, improve internal security practices, and establish credibility in domestic and international markets.
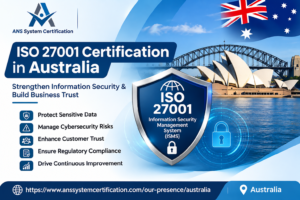
Key Benefits of ISO 27001 Certification
Implementing ISO 27001 offers several advantages for Australian organisations:
-
Improved Data Protection: Helps protect confidential business and customer information against unauthorised access, loss, and misuse.
-
Risk Management: Identifies potential information security threats and establishes suitable measures to minimise risks.
-
Customer Trust: Demonstrates a commitment to maintaining strong information security practices.
-
Regulatory Support: Helps organisations manage information security responsibilities and support compliance with applicable legal and regulatory requirements.
-
Business Opportunities: Strengthens business credibility and can help organisations meet information security requirements when working with clients and international partners.
-
Operational Efficiency: Establishes consistent security procedures, responsibilities, and monitoring processes.
ISO 27001 Certification Process in Australia
Organisations planning to achieve certification should follow a structured implementation and assessment process. The typical steps include:
-
Initial Assessment: Review existing information security practices and identify gaps against ISO 27001 requirements.
-
Risk Assessment: Identify information security risks, evaluate their potential impact, and determine appropriate treatment measures.
-
ISMS Implementation: Develop information security policies, procedures, controls, and documentation.
-
Employee Awareness: Train employees to understand their information security responsibilities.
-
Internal Audit: Evaluate the effectiveness of the implemented Information Security Management System.
-
Management Review: Assess ISMS performance and identify opportunities for improvement.
-
Certification Audit: An independent certification body conducts the required audit to determine conformity with ISO 27001 requirements.
-
Certification and Maintenance: Following successful certification, organisations continue monitoring and improving their ISMS through surveillance audits and ongoing improvements.
Why Choose ANS System Certification?
Selecting an experienced certification body is an important consideration for organisations seeking ISO certification. ANS System Certification supports businesses in understanding certification requirements and progressing through the certification assessment process.
Organisations looking for ISO 27001 Certification Australia can explore the services and certification information provided by ANS System Certification. Its website offers further details about its presence and certification services in Australia.
Conclusion
Information security is essential for building a sustainable and trustworthy business in Australia’s competitive marketplace. ISO 27001 Certification Australia provides organisations with a recognised framework to manage information security risks, protect sensitive data, and improve business resilience. By implementing ISO 27001, businesses can strengthen their security practices, increase customer confidence, and demonstrate their commitment to protecting valuable information assets.